ISO/IEC 27028:2026 provides guidance on using information security control attributes. Here is what the publication confirms—and what teams should check before changing their approach.
Source published: 2026-11-11
Audience / jurisdiction: International; no jurisdiction-specific legal adoption established
New guidance on using control attributes
ISO’s catalogue lists ISO/IEC 27028:2026, Information security, cybersecurity and privacy protection — Guidance on using information security control attributes, as a published first edition. Its lifecycle record gives 11 November 2026 as the publication date, placing the release within the current reporting window.
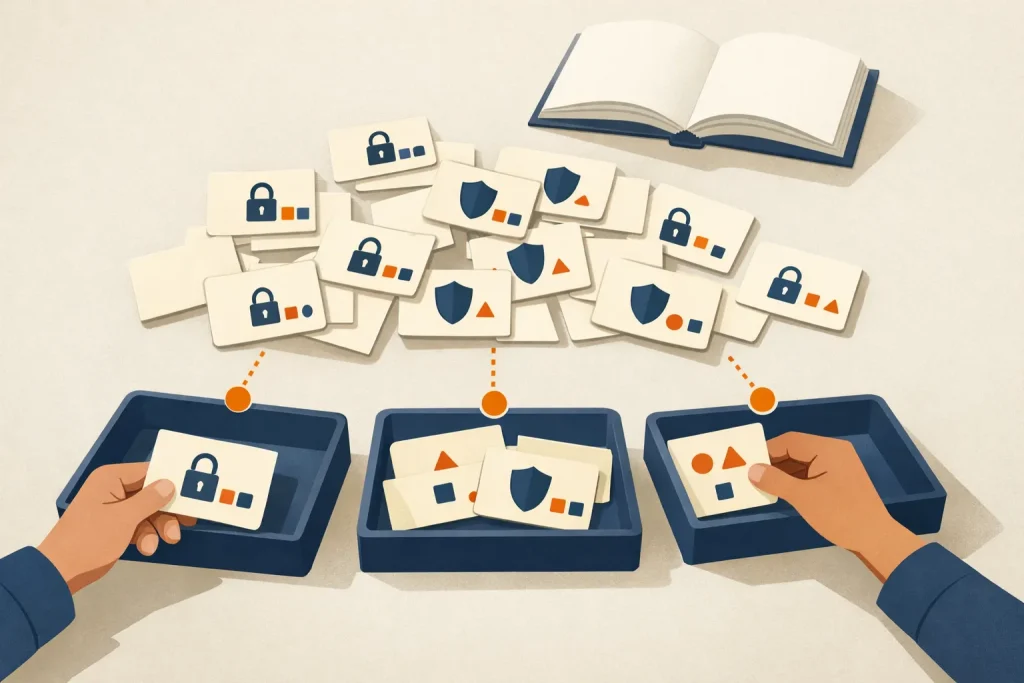
The standard provides guidance on using the information security control attributes specified in ISO/IEC 27002. For practitioners, the immediate question is whether reviewing that guidance could make existing control information more useful—not whether publication alone requires a new compliance programme.
Sources: [1]
Who should assess its relevance?
The catalogue states that the guidance applies to organizations of any type, size or nature. Information security managers, control owners and internal auditors are therefore a practical readership, particularly where teams already maintain a control register and want to examine how its information is organized.
An editorial starting point is to identify a decision that better-organized control information should support. For example, a team might want a clearer view of which controls need management attention. This is a hypothetical use case, not a result promised by the standard or a verified description of its detailed recommendations.
The useful test is whether a proposed approach helps people interpret and use the information they already hold. Adding fields to a register without a defined purpose should not be treated as the objective.
Sources: [1]
Publication is not a compliance deadline
The public record identifies edition 1, published status and lifecycle stage 60.60. It names ISO/IEC JTC 1/SC 27 as the responsible committee. These details support treating the release as a published standard rather than a consultation draft.
The catalogue publication field gives November 2026, while the lifecycle record supplies the more precise date of 11 November. Neither should be presented as a legal effective date. The public page states no effective date or transition deadline, and the evidence establishes no jurisdiction-specific legal adoption.
The source describes guidance. It does not support a claim that every organization must implement ISO/IEC 27028 or revise its controls immediately.
Sources: [1]
What remains to be checked
The full standard was not reviewed for this article. The catalogue supports the publication announcement and its broad scope, but not detailed conclusions about recommended methods, individual clauses or changes needed in an organization’s existing arrangements.
Before approving implementation work, practitioners should obtain and review the published text against their own objectives. In particular, do not infer from the title alone that existing control descriptions, audit criteria or reporting formats must change. Any such decision needs a more specific basis than the catalogue announcement.
Sources: [1]
Practical next steps
As editorial suggestions rather than stated requirements, begin by locating where control attributes are currently recorded and identifying who maintains that information. Ask control owners and auditors which questions their present views answer well and where they struggle.
After reviewing the guidance, pilot any proposed changes on a small selection of controls. Compare the effort needed to maintain the information with the usefulness of the resulting views. Record why a change is being proposed, who would own it and how the team would judge its value.
This keeps the response proportionate: assess the new guidance, test a specific improvement and expand only where the evidence supports doing so.
Which decision would your team make more effectively if its security controls could be consistently grouped by attributes?
Sources: [1]
Sources
Your experience
Which decision would your team make more effectively if its security controls could be consistently grouped by attributes?